
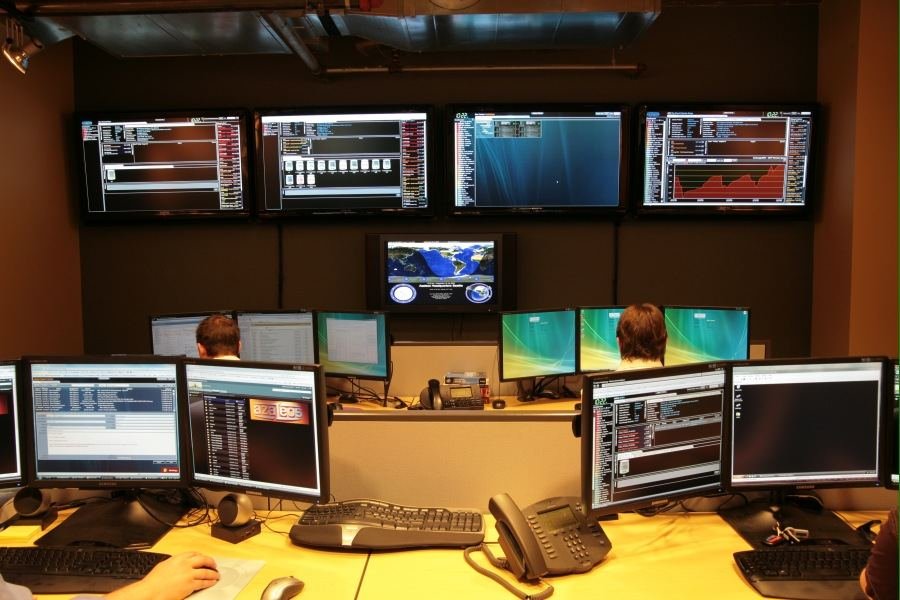
Security operations centres are the quiet watchtowers of modern business, rooms where analysts monitor networks around the clock for signs of attack. Every email, login and file transfer leaves a trace, and the centre’s job is to separate ordinary activity from the patterns that signal trouble. Screens show traffic flowing in and out of company systems, with automated tools flagging anything unusual for a human to examine. The work demands patience and judgement, since most alerts turn out to be harmless and the real threats hide among them. Analysts learn the normal rhythm of their organisation, so a login at an odd hour or a sudden flood of data stands out quickly. When something genuine is found, the team moves fast, isolating affected machines and alerting colleagues before damage spreads. For businesses that depend on digital systems, the operations centre has become as essential as locks on the doors, protecting data that customers trust them to keep safe.
What the Evidence Shows
Running an effective centre is as much about people and process as it is about technology. New analysts start with routine alerts and learn from experienced colleagues how to investigate without causing false alarms. Playbooks set out the steps for common incidents, so the team responds the same way whether it is a weekday morning or the middle of the night. Regular exercises simulate attacks, testing how quickly the team notices and how well different departments work together under pressure. Communication matters too, because a technical finding must be explained clearly to managers who decide what to tell customers and regulators. Smaller firms that cannot staff a full centre often share one, buying monitoring as a service from a specialist provider. The threats keep evolving, with attackers trying new tricks every month, but a well-run operations centre gives a business a fighting chance to spot trouble early and limit the harm. Reporting and analysis from sources such as Wired track the same developments, and specialists following security operations centres say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is an industry learning to ship capability and restraint together. Products built around security operations centres now launch with safety evaluations, usage data and rollback plans as standard, because enterprise buyers and regulators ask for them in the first meeting. Companies that treated those questions as friction are discovering they have become the purchase criteria.
What Happens Next
What happens next for security operations centres depends less on another breakthrough than on the unglamorous work of reliability, pricing and support. The buyers evaluating it now are not enthusiasts; they are operators with budgets and auditors, and their checklists will decide the timeline. On the evidence of the current pilots, the technology has earned the right to be judged by them. You can follow related developments in our coverage of technology.
None of this will be settled by a single announcement, study or product launch. The pattern to watch is accumulation: independent confirmations, honest reporting of failures and steady improvement in the underlying numbers. Readers who follow those signals, rather than the loudest claim of the week, will understand this subject better than most of the commentary surrounding it suggests is possible.
